
Proper study guides for Improved CompTIA CompTIA PenTest+ Certification Exam certified begins with CompTIA PT0-002 preparation products which designed to deliver the Certified PT0-002 questions by making you pass the PT0-002 test at your first time. Try the free PT0-002 demo right now.
Also have PT0-002 free dumps questions for you:
NEW QUESTION 1
Given the following script: while True:
print ("Hello World")
Which of the following describes True?
- A. A while loop
- B. A conditional
- C. A Boolean operator
- D. An arithmetic operator
Answer: C
Explanation:
True is a Boolean operator in Python, which is an operator that returns either True or False values based on logical conditions. Boolean operators can be used in expressions or statements that evaluate to True or False values, such as comparisons, assignments, or loops. In the code, True is used as the condition for a while loop, which is a loop that repeats a block of code as long as the condition is True. The code will print “Hello World” indefinitely because True will always be True and the loop will never end. The other options are not valid descriptions of True.
NEW QUESTION 2
A penetration tester downloaded the following Perl script that can be used to identify vulnerabilities in network switches. However, the script is not working properly.
Which of the following changes should the tester apply to make the script work as intended?
- A. Change line 2 to $ip= €10.192.168.254€;
- B. Remove lines 3, 5, and 6.
- C. Remove line 6.
- D. Move all the lines below line 7 to the top of the script.
Answer: B
Explanation:
https://www.asc.ohio-state.edu/lewis.239/Class/Perl/perl.html Example script:
#!/usr/bin/perl
$ip=$argv[1]; attack($ip);
sub attack { print("x");
}
NEW QUESTION 3
During a penetration tester found a web component with no authentication requirements. The web component also allows file uploads and is hosted on one of the target public web the following actions should the penetration tester perform next?
- A. Continue the assessment and mark the finding as critical.
- B. Attempting to remediate the issue temporally.
- C. Notify the primary contact immediately.
- D. Shutting down the web server until the assessment is finished
Answer: C
Explanation:
The penetration tester should notify the primary contact immediately, as this is a serious security issue that may compromise the confidentiality, integrity, and availability of the web server and its data. A web component with no authentication requirements and file upload capabilities can allow an attacker to upload malicious files, such as web shells, backdoors, or malware, to the web server and gain remote access or execute arbitrary commands on the web server. This can lead to further attacks, such as data theft, data corruption, privilege escalation, lateral movement, or denial of service. The penetration tester should inform the primary contact of the issue and its potential impact, and provide recommendations for remediation, such as implementing authentication mechanisms, restricting file upload types and sizes, or scanning uploaded files for malware. The other options are not appropriate actions for the penetration tester at this stage. Continuing the assessment and marking the finding as critical would delay the notification and remediation of the issue, which may increase the risk of exploitation by other attackers. Attempting to remediate the issue temporarily would interfere with the normal operation of the web server and may cause unintended consequences or damage. Shutting down the web server until the assessment is finished would disrupt the availability of the web server and its services, and may violate the scope or agreement of the assessment.
NEW QUESTION 4
Which of the following tools would be MOST useful in collecting vendor and other security-relevant information for IoT devices to support passive reconnaissance?
- A. Shodan
- B. Nmap
- C. WebScarab-NG
- D. Nessus
Answer: B
NEW QUESTION 5
A penetration tester gains access to a system and is able to migrate to a user process: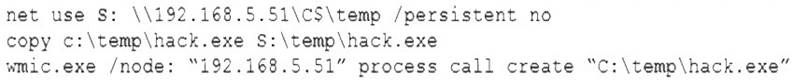
Given the output above, which of the following actions is the penetration tester performing? (Choose two.)
- A. Redirecting output from a file to a remote system
- B. Building a scheduled task for execution
- C. Mapping a share to a remote system
- D. Executing a file on the remote system
- E. Creating a new process on all domain systems
- F. Setting up a reverse shell from a remote system
- G. Adding an additional IP address on the compromised system
Answer: CD
Explanation:
WMIC.exe is a built-in Microsoft program that allows command-line access to the Windows Management Instrumentation. Using this tool, administrators can query the operating system for detailed information about installed hardware and Windows settings, run management tasks, and even execute other programs or commands.
NEW QUESTION 6
Which of the following tools should a penetration tester use to crawl a website and build a wordlist using the data recovered to crack the password on the website?
- A. DirBuster
- B. CeWL
- C. w3af
- D. Patator
Answer: B
Explanation:
CeWL, the Custom Word List Generator, is a Ruby application that allows you to spider a website based on a URL and depth setting and then generate a wordlist from the files and web pages it finds. Running CeWL against a target organization’s sites can help generate a custom word list, but you will typically want to add words manually based on your own OSINT gathering efforts.
https://esgeeks.com/como-utilizar-cewl/
NEW QUESTION 7
A penetration tester is attempting to discover live hosts on a subnet quickly. Which of the following commands will perform a ping scan?
- A. nmap -sn 10.12.1.0/24
- B. nmap -sV -A 10.12.1.0/24
- C. nmap -Pn 10.12.1.0/24
- D. nmap -sT -p- 10.12.1.0/24
Answer: A
NEW QUESTION 8
A penetration tester has completed an analysis of the various software products produced by the company under assessment. The tester found that over the past several years the company has been including vulnerable third-party modules in multiple products, even though the quality of the organic code being developed is very good. Which of the following recommendations should the penetration tester include in the report?
- A. Add a dependency checker into the tool chain.
- B. Perform routine static and dynamic analysis of committed code.
- C. Validate API security settings before deployment.
- D. Perform fuzz testing of compiled binaries.
Answer: A
Explanation:
Adding a dependency checker into the tool chain is the best recommendation for the company that has been including vulnerable third-party modules in multiple products. A dependency checker is a tool that analyzes the dependencies of a software project and identifies any known vulnerabilities or outdated versions. This can help the developers to update or replace the vulnerable modules before deploying the products.
NEW QUESTION 9
Which of the following BEST describes why a client would hold a lessons-learned meeting with the penetration-testing team?
- A. To provide feedback on the report structure and recommend improvements
- B. To discuss the findings and dispute any false positives
- C. To determine any processes that failed to meet expectations during the assessment
- D. To ensure the penetration-testing team destroys all company data that was gathered during the test
Answer: C
NEW QUESTION 10
During a penetration test, the domain names, IP ranges, hosts, and applications are defined in the:
- A. SOW.
- B. SLA.
- C. ROE.
- D. NDA
Answer: C
Explanation:
https://mainnerve.com/what-are-rules-of-engagement-in-pen-testing/#:~:text=The%20ROE%20includes%20the
NEW QUESTION 11
A penetration tester has gained access to part of an internal network and wants to exploit on a different network segment. Using Scapy, the tester runs the following command: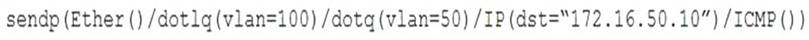
Which of the following represents what the penetration tester is attempting to accomplish?
- A. DNS cache poisoning
- B. MAC spoofing
- C. ARP poisoning
- D. Double-tagging attack
Answer: D
Explanation:
https://scapy.readthedocs.io/en/latest/usage.html
NEW QUESTION 12
Which of the following should a penetration tester do NEXT after identifying that an application being tested has already been compromised with malware?
- A. Analyze the malware to see what it does.
- B. Collect the proper evidence and then remove the malware.
- C. Do a root-cause analysis to find out how the malware got in.
- D. Remove the malware immediately.
- E. Stop the assessment and inform the emergency contact.
Answer: E
Explanation:
Stopping the assessment and informing the emergency contact is the best thing to do next after identifying that an application being tested has already been compromised with malware. This is because continuing the assessment might interfere with an ongoing investigation or compromise evidence collection. The emergency contact is the person designated by the client who should be notified in case of any critical issues or incidents during the penetration testing engagement.
NEW QUESTION 13
A penetration tester conducted a discovery scan that generated the following: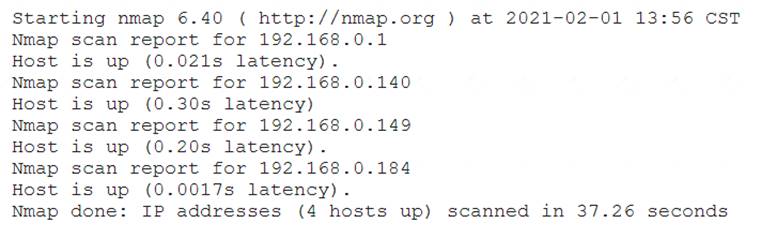
Which of the following commands generated the results above and will transform them into a list of active hosts for further analysis?
- A. nmap –oG list.txt 192.168.0.1-254 , sort
- B. nmap –sn 192.168.0.1-254 , grep “Nmap scan” | awk ‘{print S5}’
- C. nmap –-open 192.168.0.1-254, uniq
- D. nmap –o 192.168.0.1-254, cut –f 2
Answer: B
Explanation:
the NMAP flag (-sn) which is for host discovery and returns that kind of NMAP output. And the AWK command selects column 5 ({print $5}) which obviously carries the returned IP of the host in the NMAP output.
This command will generate the results shown in the image and transform them into a list of active hosts for further analysis. The command consists of three parts: nmap -sn 192.168.0.1-254: This part uses nmap, a network scanning tool, to perform a ping scan (-sn) on the IP range 192.168.0.1-254, which means sending ICMP echo requests to each IP address and checking if they respond. grep “Nmap scan”: This part uses grep, a text filtering tool, to search for the string “Nmap scan” in the output of the previous part and display only the matching lines. This will filter out the lines that show the start and end time of the scan and only show the lines that indicate the status of each host. awk ‘{print $5}’: This part uses awk, a text processing tool, to print the fifth field ($5) of each line in the output of the previous part. This will extract only the IP addresses of each host and display them as a list.
The final output will look something like this: 192.168.0.1 192.168.0.12 192.168.0.17 192.168.0.34
NEW QUESTION 14
A software development team is concerned that a new product's 64-bit Windows binaries can be deconstructed to the underlying code. Which of the following tools can a penetration tester utilize to help the team gauge what an attacker might see in the binaries?
- A. Immunity Debugger
- B. OllyDbg
- C. GDB
- D. Drozer
Answer: A
Explanation:
Immunity Debugger is a tool that can be used to deconstruct 64-bit Windows binaries and see the underlying code. Immunity Debugger is a powerful debugger that integrates with Python and allows users to write their own scripts and plugins. It can be used for reverse engineering, malware analysis, vulnerability research, and exploit development
NEW QUESTION 15
A penetration tester gives the following command to a systems administrator to execute on one of the target servers:
rm -f /var/www/html/G679h32gYu.php
Which of the following BEST explains why the penetration tester wants this command executed?
- A. To trick the systems administrator into installing a rootkit
- B. To close down a reverse shell
- C. To remove a web shell after the penetration test
- D. To delete credentials the tester created
Answer: C
Explanation:
s for why the penetration tester wants this command executed.
NEW QUESTION 16
Which of the following BEST explains why a penetration tester cannot scan a server that was previously scanned successfully?
- A. The IP address is wrong.
- B. The server is unreachable.
- C. The IP address is on the blocklist.
- D. The IP address is on the allow list.
Answer: C
Explanation:
for why a penetration tester cannot scan a server that was previously scanned successfully is that the IP address is on the blocklist. Blocklists are used to prevent malicious actors from scanning servers, and if the IP address of the server is on the blocklist, the scanning process will be blocked.
NEW QUESTION 17
A consultant just performed a SYN scan of all the open ports on a remote host and now needs to remotely identify the type of services that are running on the host. Which of the following is an active reconnaissance tool that would be BEST to use to accomplish this task?
- A. tcpdump
- B. Snort
- C. Nmap
- D. Netstat
- E. Fuzzer
Answer: C
NEW QUESTION 18
You are a penetration tester reviewing a client’s website through a web browser. INSTRUCTIONS
Review all components of the website through the browser to determine if vulnerabilities are present. Remediate ONLY the highest vulnerability from either the certificate, source, or cookies.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.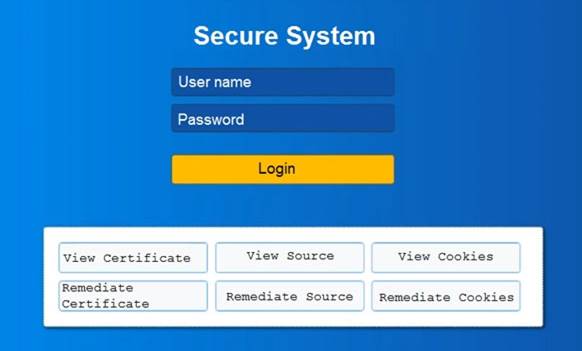
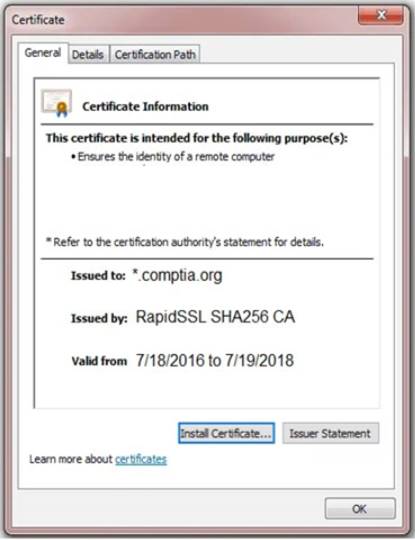
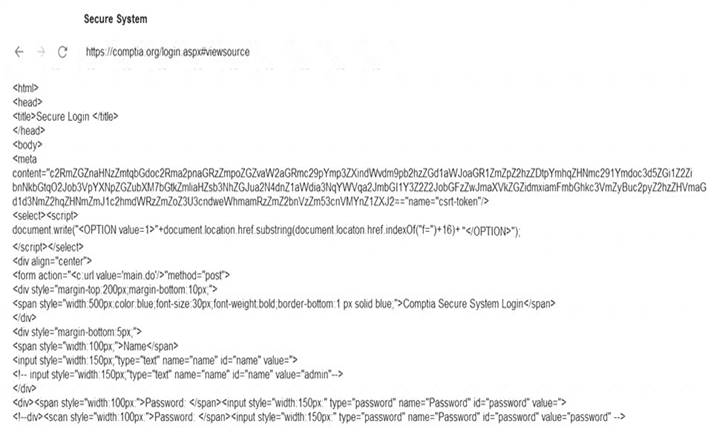
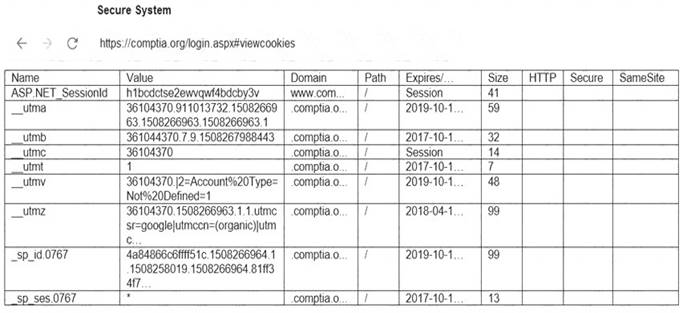
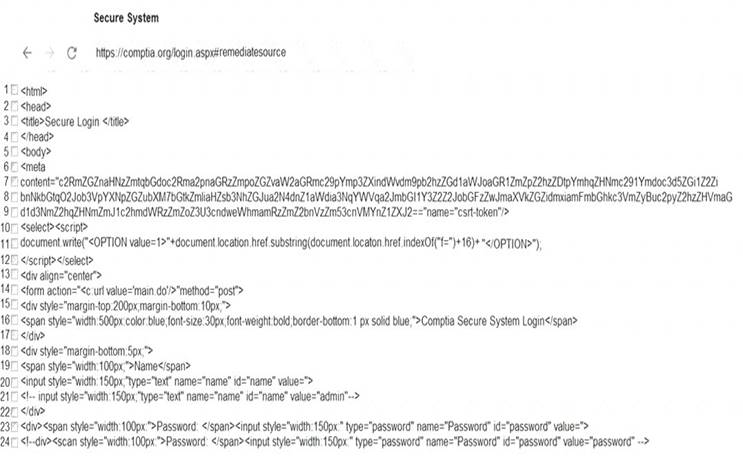
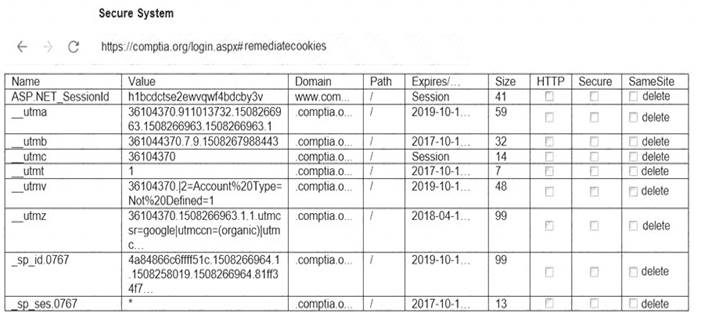
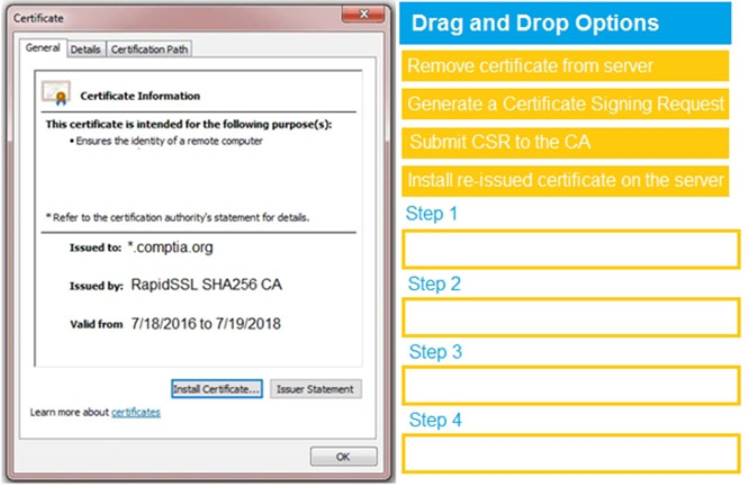
Solution:
Graphical user interface Description automatically generated
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 19
......
P.S. Surepassexam now are offering 100% pass ensure PT0-002 dumps! All PT0-002 exam questions have been updated with correct answers: https://www.surepassexam.com/PT0-002-exam-dumps.html (278 New Questions)
