
We provide real SC-300 exam questions and answers braindumps in two formats. Download PDF & Practice Tests. Pass Microsoft SC-300 Exam quickly & easily. The SC-300 PDF type is available for reading and printing. You can print more and practice many times. With the help of our Microsoft SC-300 dumps pdf and vce product and material, you can easily pass the SC-300 exam.
Online Microsoft SC-300 free dumps demo Below:
NEW QUESTION 1
You create a new Microsoft 365 E5 tenant.
You need to ensure that when users connect to the Microsoft 365 portal from an anonymous IP address, they are prompted to use multi-factor authentication (MFA).
What should you configure?
- A. a sign-in risk policy
- B. a user risk policy
- C. an MFA registration policy
Answer: A
NEW QUESTION 2
You use Azure Monitor to analyze Azure Active Directory (Azure AD) activity logs.
Yon receive more than 100 email alerts each day for tailed Azure Al) user sign-in attempts. You need to ensure that a new security administrator receives the alerts instead of you. Solution: From Azure monitor, you modify the action group.
Does this meet the goal?
- A. Yes
- B. No
Answer: B
NEW QUESTION 3
You have an Azure Active Directory (Azure AD) tenant.
You need to review the Azure AD sign-ins log to investigate sign ins that occurred in the past. For how long does Azure AD store events in the sign-in log?
- A. 14 days
- B. 30 days
- C. 90 days
- D. 365 days
Answer: B
NEW QUESTION 4
You need to modify the settings of the User administrator role to meet the technical requirements. Which two actions should you perform for the role? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A. Select Require justification on activation
- B. Set all assignments to Active
- C. Set all assignments to Eligible
- D. Modify the Expire eligible assignments after setting.
- E. Select Require ticket information on activation.
Answer: AB
NEW QUESTION 5
You have an Azure Active Directory (Azure AD) tenant that contains three users named User1, User1, and User3,
You create a group named Group1. You add User2 and User3 to Group1.
You configure a role in Azure AD Privileged identity Management (PIM) as shown in the application administrator exhibit. (Click the application Administrator tab.)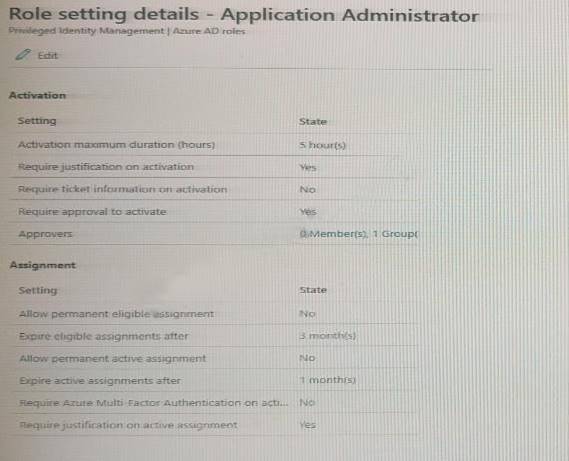
Group1 is configured as the approver for the application administrator role. You configure User2to be eligible for the application administrator role.
For User1, you add an assignment to the Application administrator role as shown in the Assignment exhibit. (Click Assignment tab)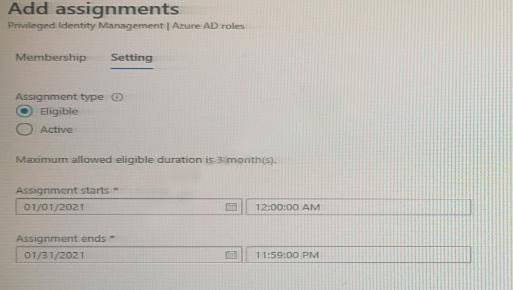
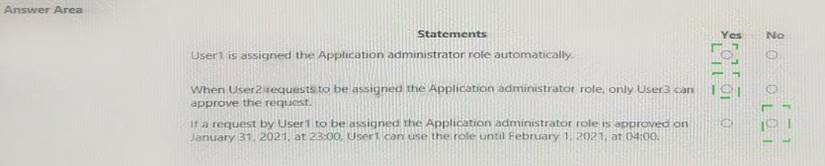
For each of the following statement, select Yes if the statement is true, Otherwise, select No. NOTE: Each correct selection is worth one point.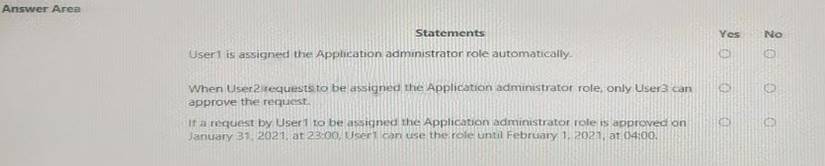
Solution:
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 6
You have an Azure Active Directory (Azure AD) tenant that has the default App registrations settings. The tenant contains the users shown in the following table.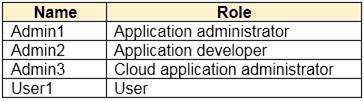
You purchase two cloud apps named App1 and App2. The global administrator registers App1 in Azure AD. You need to identify who can assign users to App1, and who can register App2 in Azure AD.
What should you identify? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.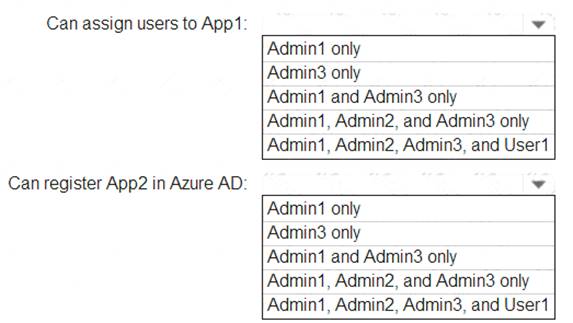
Solution:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/manage-apps/add-application-portal-assign-users https://docs.microsoft.com/en-us/azure/active-directory/develop/active-directory-how-applications-are-added
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 7
You need to implement the planned changes for litware.com. What should you configure?
- A. Azure AD Connect cloud sync between the Azure AD tenant and litware.com
- B. Azure AD Connect to include the litware.com domain
- C. staging mode in Azure AD Connect for the litware.com domain
Answer: C
NEW QUESTION 8
Your company has a Microsoft 365 tenant.
The company has a call center that contains 300 users. In the call center, the users share desktop computers and might use a different computer every day. The call center computers are NOT configured for biometric identification.
The users are prohibited from having a mobile phone in the call center.
You need to require multi-factor authentication (MFA) for the call center users when they access Microsoft 365 services.
What should you include in the solution?
- A. a named network location
- B. the Microsoft Authenticator app
- C. Windows Hello for Business authentication
- D. FIDO2 tokens
Answer: D
Explanation:
https://docs.microsoft.com/en-us/azure/active-directory/authentication/concept-authentication-passwordless
NEW QUESTION 9
You configure a new Microsoft 36S tenant to use a default domain name of contosso.com.
You need to ensure that you can control access to Microsoft 365 resource-, by using conditional access policy. What should you do first?
- A. Disable the User consent settings.
- B. Disable Security defaults.
- C. Configure a multi-factor authentication (Ml A) registration policy1.
- D. Configure password protection for Windows Server Active Directory.
Answer: B
NEW QUESTION 10
You have a custom cloud app named App1 that is registered in Azure Active Directory (Azure AD). App1 is configured as shown in the following exhibit.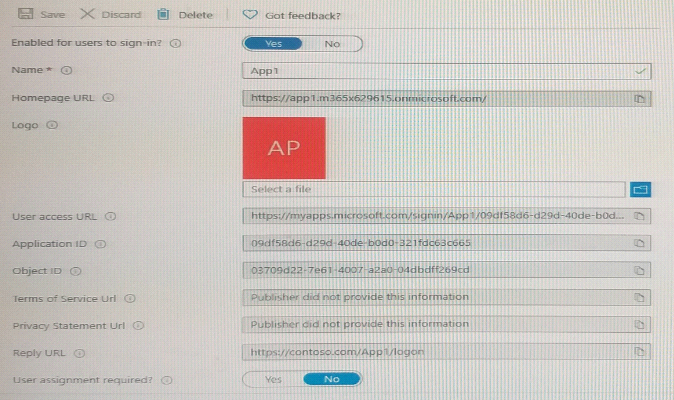
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.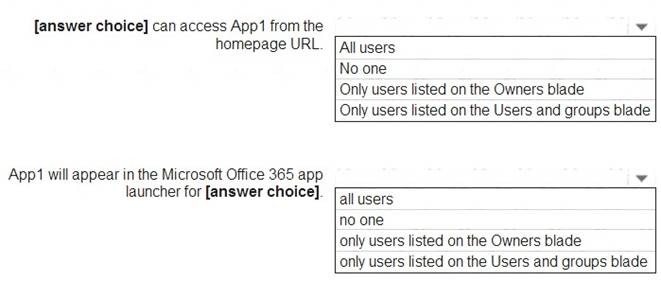
Solution:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/manage-apps/assign-user-or-group-access-portal
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 11
Your network contains an Active Directory forest named contoso.com that is linked to an Azure Active Directory (Azure AD) tenant named contoso.com by using Azure AD Connect.
Attire AD Connect is installed on a server named Server 1.
You deploy a new server named Server? that runs Windows Server 2019.
You need to implement a failover server for Azure AD Connect. The solution must minimize how long it takes to fail over if Server1 fails.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.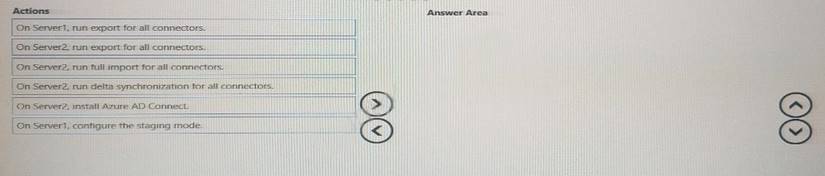
Solution:
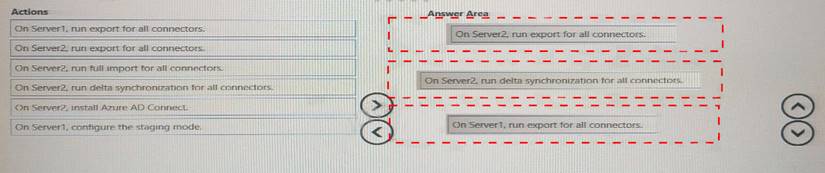
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 12
You have an Azure Active Directory (Azure AD) tenant.
You create an enterprise application collection named HR Apps that has the following settings:
• Applications: Appl. App?, App3
• Owners: Admin 1
• Users and groups: HRUsers
AH three apps have the following Properties settings:
• Enabled for users to sign in: Yes
• User assignment required: Yes
• Visible to users: Yes
Users report that when they go to the My Apps portal, they only sue App1 and App2-You need to ensure that the users can also see App3. What should you do from App3?
What should you do from App3?
- A. From Users and groups, add HRUsers.
- B. Prom Properties, change User assignment required to No.
- C. From Permissions, review the User consent permissions.
- D. From Single sign on, configure a sign-on method.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/manage-apps/assign-user-or-group-access-portal https://docs.microsoft.com/en-us/azure/active-directory/user-help/my-applications-portal-workspaces
NEW QUESTION 13
Your company has two divisions named Contoso East and Contoso West. The Microsoft 365 identity architecture tor both divisions is shown in the following exhibit.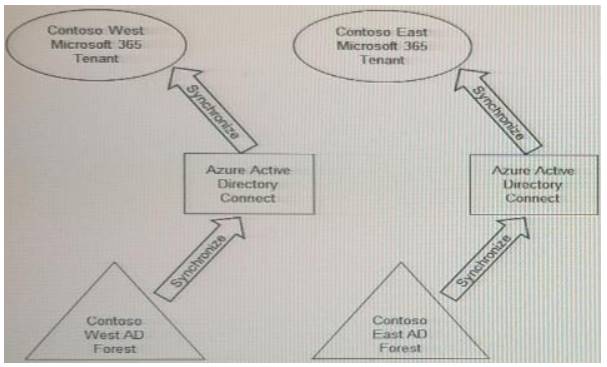
You need to assign users from the Contoso East division access to Microsoft SharePoint Online sites in the Contoso West tenant. The solution must not require additional Microsoft 3G5 licenses.
What should you do?
- A. Configure the exiting Azure AD Connect server in Contoso Cast to sync the Contoso East ActiveDirectory forest to the Contoso West tenant.
- B. Configure Azure AD Application Proxy in the Contoso West tenant.
- C. Deploy a second Azure AD Connect server to Contoso East and configure the server to sync the Contoso East Active Directory forest to the Contoso West tenant.
- D. Invite the Contoso East users as guests in the Contoso West tenant.
Answer: D
NEW QUESTION 14
You have a Microsoft 365 tenant.
You currently allow email clients that use Basic authentication to conned to Microsoft Exchange Online.
You need to ensure that users can connect t to Exchange only run email clients that use Modern authentication protocols.
What should you implement?
You need to ensure that use Modern authentication
- A. a compliance policy in Microsoft Endpoint Manager
- B. a conditional access policy in Azure Active Directory (Azure AD)
- C. an application control profile in Microsoft Endpoint Manager
- D. an OAuth policy in Microsoft Cloud App Security
Answer: C
NEW QUESTION 15
You have a Microsoft 365 tenant.
The Sign-ins activity report shows that an external contractor signed in to the Exchange admin center. You need to review access to the Exchange admin center at the end of each month and block sign-ins if required.
What should you create?
- A. an access package that targets users outside your directory
- B. an access package that targets users in your directory
- C. a group-based access review that targets guest users
- D. an application-based access review that targets guest users
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/governance/access-reviews-overview
NEW QUESTION 16
You need to meet the technical requirements for the probability that user identifies were compromised. What should the users do first, and what should you configure? To answer, select the appropriate options in
the answer area.
NOTE: Each correct selection is worth one point.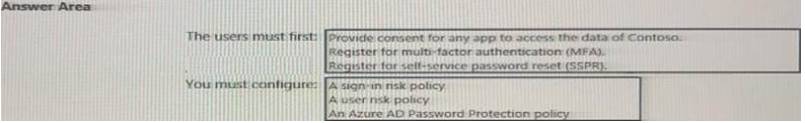
Solution:
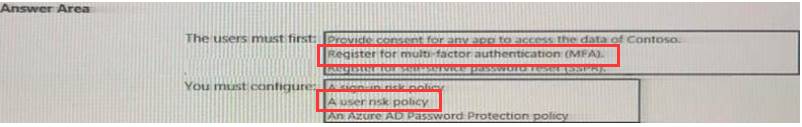
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 17
You have an Azure Active Directory (Azure AD) tenant that has Security defaults disabled. You are creating a conditional access policy as shown in the following exhibit.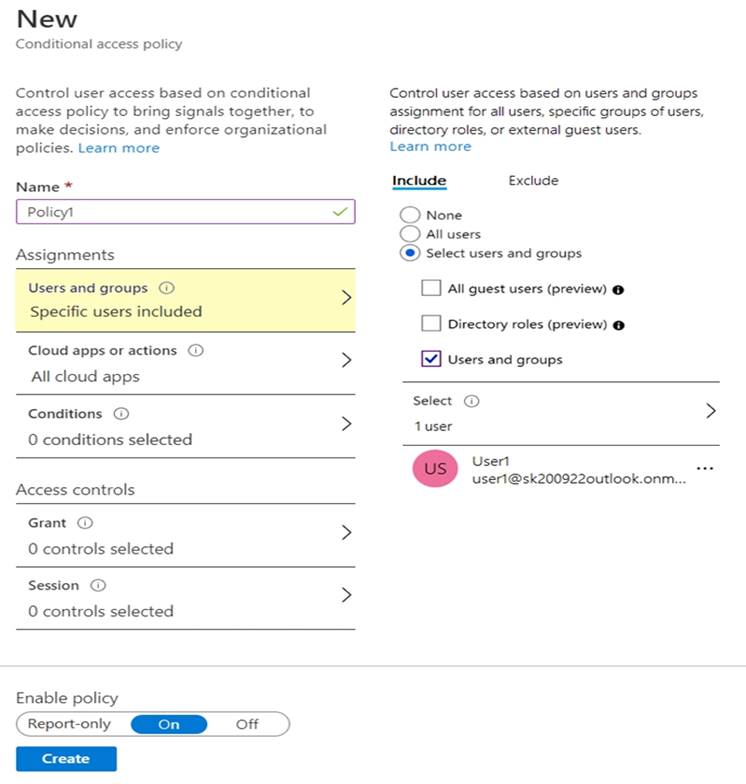
Use the drop-down menus to select the answer choice that completes each statement based on the information
presented in the graphic.
NOTE: Each correct selection is worth one point.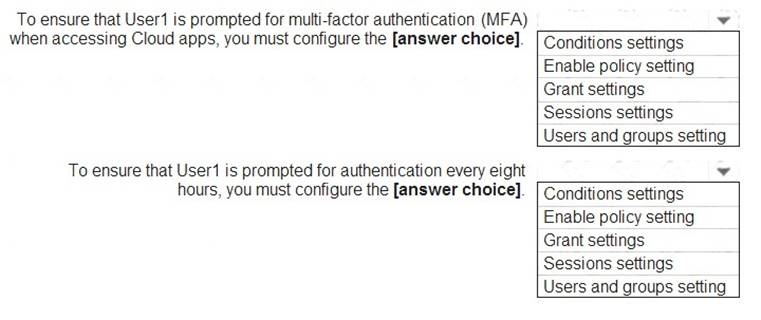
Solution:
Reference:
https://docs.microsoft.com/en-us/azure/active-directory/conditional-access/howto-conditional-access-policy-all
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 18
......
Recommend!! Get the Full SC-300 dumps in VCE and PDF From Downloadfreepdf.net, Welcome to Download: https://www.downloadfreepdf.net/SC-300-pdf-download.html (New 192 Q&As Version)
