
Want to know Pass4sure az-500 Exam practice test features? Want to lear more about Microsoft Microsoft Azure Security Technologies certification experience? Study Actual Microsoft az-500 answers to Improve az-500 questions at Pass4sure. Gat a success with an absolute guarantee to pass Microsoft az-500 (Microsoft Azure Security Technologies) test on your first attempt.
Free demo questions for Microsoft az-500 Exam Dumps Below:
NEW QUESTION 1
You have an Azure subscription that contains the virtual machines shown in the following table.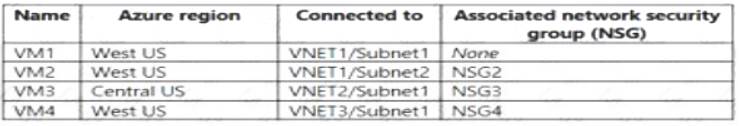
VNET1, VNET2, and VNET3 are peered with each other. You perform the following actions:
* Create two application security groups named ASG1 and ASG2 in the West US region.
* Add the network interface of VM1 to ASG1.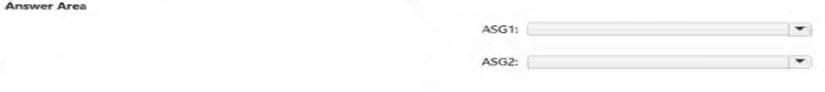
Solution:
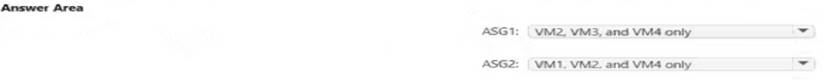
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 2
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You use Azure Security Center for the centralized policy management of three Azure subscriptions. You use several policy definitions to manage the security of the subscriptions.
You need to deploy the policy definitions as a group to all three subscriptions.
Solution: You create an initiative and an assignment that is scoped to a management group. Does this meet the goal?
- A. Yes
- B. No
Answer: A
Explanation:
References:
https://docs.microsoft.com/en-us/azure/governance/policy/overview
NEW QUESTION 3
You onboard Azure Sentinel. You connect Azure Sentinel to Azure Security Center.
You need to automate the mitigation of incidents in Azure Sentinel. The solution must minimize administrative effort.
What should you create?
- A. an alert rule
- B. a playbook
- C. a function app
- D. a runbook
Answer: B
NEW QUESTION 4
You have an Azure Active Directory (Azure AD) tenant that contains the users shown in the following table.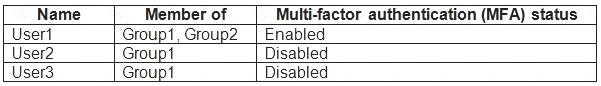
You create and enforce an Azure AD Identity Protection sign-in risk policy that has the following settings:  Assignments: Include Group1, exclude Group2 Conditions: Sign-in risk level: Medium and above Access Allow access, Require multi-factor authentication
You need to identify what occurs when the users sign in to Azure AD.
What should you identify for each user? To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.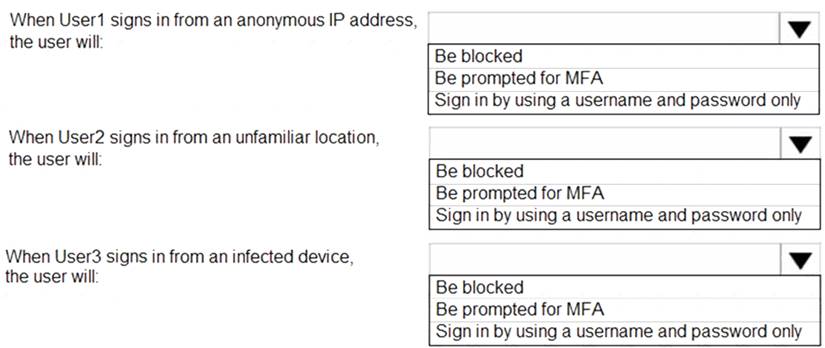
Solution:
References:
http://www.rebeladmin.com/2018/09/step-step-guide-configure-risk-based-azure-conditional-access-policies/ https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/concept-identity-protection-policies https://docs.microsoft.com/en-us/azure/active-directory/identity-protection/concept-identity-protection-risks
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 5
You have an Azure subscription that contains a virtual network. The virtual network contains the subnets shown in the following table.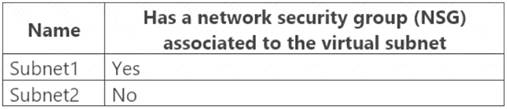
The subscription contains the virtual machines shown in the following table.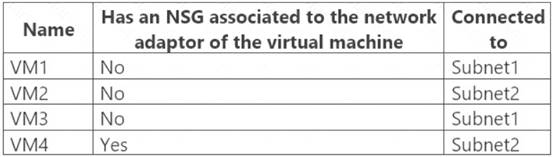
You enable just in time (JIT) VM access for all the virtual machines. You need to identify which virtual machines are protected by JIT. Which virtual machines should you identify?
- A. VM4 only
- B. VM1 and VM3 only
- C. VM1, VM3 and VM4 only
- D. VM1, VM2, VM3, and VM4
Answer: C
Explanation:
An NSG needs to be enabled, either at the VM level or the subnet level. Reference:
https://docs.microsoft.com/en-us/azure/security-center/security-center-just-in-time
NEW QUESTION 6
You create resources in an Azure subscription as shown in the following table.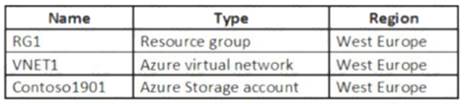
VNET1 contains two subnets named Subnet1 and Subnet2. Subnet1 has a network ID of 10.0.0.0/24. Subnet2 has a network ID of 10.1.1.0/24.
Contoso1901 is configured as shown in the exhibit. (Click the Exhibit tab.)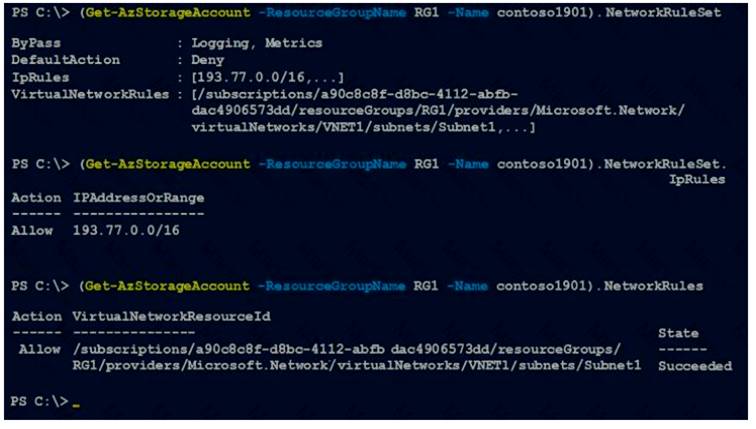
For each of the following statements, select Yes if the statement is true. Otherwise, select No. NOTE: Each correct selection is worth one point.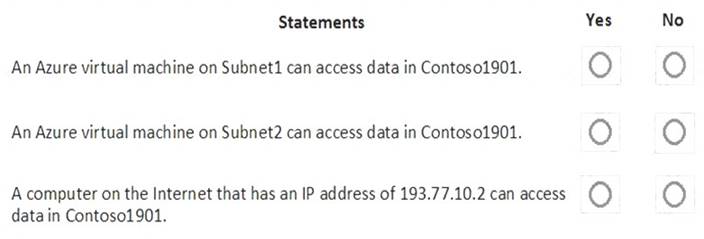
Solution:
Box 1: Yes
Access from Subnet1 is allowed. Box 2: No
No access from Subnet2 is allowed. Box 3: Yes
Access from IP address 193.77.10.2 is allowed.
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 7
You have an Azure subscription mat contains a resource group named RG1. RG1 contains a storage account named storage1.
You have two custom Azure rotes named Role1 and Role2 that are scoped to RG1. The permissions for Role1 are shown in the following JSON code.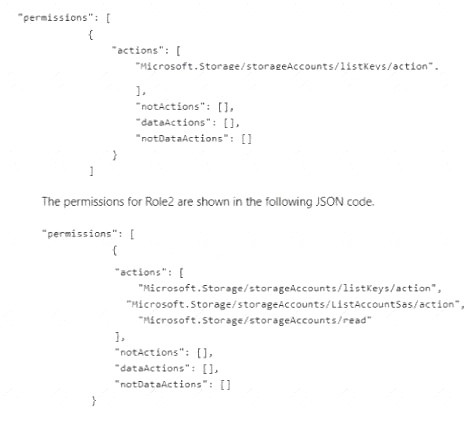
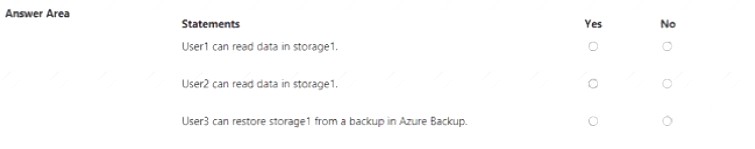
Solution:
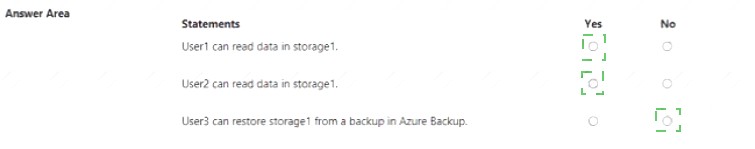
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 8
You have an Azure subscription that contains a storage account named storage1 and several virtual machines. The storage account and virtual machines are in the same Azure region. The network configurations of the virtual machines are shown in the following table.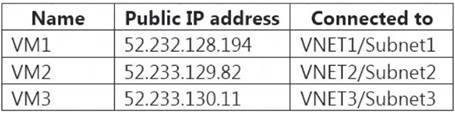
The virtual network subnets have service endpoints defined as shown in the following table.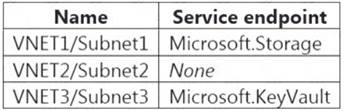
You configure the following Firewall and virtual networks settings for storage1:  Allow access from: Selected networks Virtual networks: VNET3\Subnet3 Firewall – Address range: 52.233.129.0/24
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.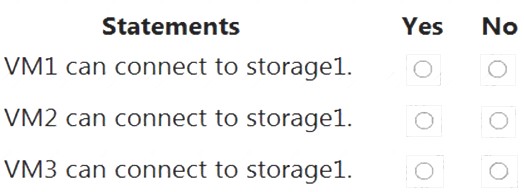
Solution:
Box 1: No
VNet1 has a service endpoint configure for Azure Storage. However, the Azure storage does not allow access from VNet1 or the public IP address of VM1.
Box 2: Yes
VNet2 does not have a service endpoint configured. However, the Azure storage allows access from the public IP address of VM2.
Box 3: No
Azure storage allows access from VNet3. However, VNet3 does not have a service endpoint for Azure storage. The Azure storage also does not allow access from the public IP of VM3.
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 9
You have an Azure subscription named Sub1 that is associated to an Azure Active Directory (Azure AD) tenant named contoso.com.
An administrator named Admin1 has access to the following identities: An OpenID-enabled user account A Hotmail account An account in contoso.com An account in an Azure AD tenant named fabrikam.com
You plan to use Azure Account Center to transfer the ownership of Sub1 to Admin1. To which accounts can you transfer the ownership of Sub1?
- A. contoso.com only
- B. contoso.com, fabrikam.com, and Hotmail only
- C. contoso.com and fabrikam.com only
- D. contoso.com, fabrikam.com, Hotmail, and OpenID-enabled user account
Answer: C
Explanation:
When you transfer billing ownership of your subscription to an account in another Azure AD tenant, you can move the subscription to the new account's tenant. If you do so, all users, groups, or service principals who had role based access (RBAC) to manage subscriptions and its resources lose their access. Only the user in the new account who accepts your transfer request will have access to manage the resources.
Reference:
https://docs.microsoft.com/en-us/azure/billing/billing-subscription-transfer
https://docs.microsoft.com/en-us/azure/billing/billing-subscription-transfer#transferring-subscription-to-anaccou
NEW QUESTION 10
You have an Azure subscription.
You plan to create a custom role-based access control (RBAC) role that will provide permission to read the Azure Storage account.
Which property of the RBAC role definition should you configure?
- A. NotActions []
- B. DataActions []
- C. AssignableScopes []
- D. Actions []
Answer: D
Explanation:
To ‘Read a storage account’, ie. list the blobs in the storage account, you need an ‘Action’ permission. To read the data in a storage account, ie. open a blob, you need a ‘DataAction’ permission.
Reference:
https://docs.microsoft.com/en-us/azure/role-based-access-control/role-definitions
NEW QUESTION 11
You need to ensure that users can access VM0. The solution must meet the platform protection requirements. What should you do?
- A. Move VM0 to Subnet1.
- B. On Firewall, configure a network traffic filtering rule.
- C. Assign RT1 to AzureFirewallSubnet.
- D. On Firewall, configure a DNAT rule.
Answer: D
Explanation:
https://docs.microsoft.com/en-us/azure/firewall/tutorial-firewall-dnat
NEW QUESTION 12
You have an Azure subscription that contains an Azure key vault.
You need to configure maximum number of days for Which new keys are valid. The solution must minimize administrative effort.
What should you use?
- A. Key Vault properties
- B. Azure Policy
- C. Azure Purview
- D. Azure Blueprints
Answer: B
NEW QUESTION 13
You are configuring an Azure Kubernetes Service (AKS) cluster that will connect to an Azure Container Registry.
You need to use the auto-generated service principal to authenticate to the Azure Container Registry. What should you create?
- A. an Azure Active Directory (Azure AD) group
- B. an Azure Active Directory (Azure AD) role assignment
- C. an Azure Active Directory (Azure AD) user
- D. a secret in Azure Key Vault
Answer: B
Explanation:
When you create an AKS cluster, Azure also creates a service principal to support cluster operability with other Azure resources. You can use this auto-generated service principal for authentication with an ACR registry. To do so, you need to create an Azure AD role assignment that grants the cluster's service principal access to the container registry.
References:
https://docs.microsoft.com/bs-latn-ba/azure/container-registry/container-registry-auth-aks
NEW QUESTION 14
Your network contains an on-premises Active Directory domain named corp.contoso.com.
You have an Azure subscription named Sub1 that is associated to an Azure Active Directory (Azure AD) tenant named contoso.com.
You sync all on-premises identities to Azure AD.
You need to prevent users who have a givenName attribute that starts with TEST from being synced to Azure AD. The solution must minimize administrative effort.
What should you use?
- A. Synchronization Rules Editor
- B. Web Service Configuration Tool
- C. the Azure AD Connect wizard
- D. Active Directory Users and Computers
Answer: A
Explanation:
Use the Synchronization Rules Editor and write attribute-based filtering rule. References:
https://docs.microsoft.com/en-us/azure/active-directory/hybrid/how-to-connect-sync-change-the-configuration
NEW QUESTION 15
You have a web app hosted on an on-premises server that is accessed by using a URL of https://www.contoso.com. You plan to migrate the web app to Azure. You will continue to use https://www.contoso.com. You need to enable HTTPS for the Azure web app. What should you do first?
- A. Export the public key from the on-premises server and save the key as a P7b file.
- B. Export the private key from the on-premises server and save the key as a PFX file that is encrypted by using TripleDES.
- C. Export the public key from the on-premises server and save the key as a CER file.
- D. Export the private key from the on-premises server and save the key as a PFX file that is encrypted by using AES256.
Answer: B
Explanation:
https://docs.microsoft.com/en-us/azure/app-service/configure-ssl-certificate#private-certificate-requirements
NEW QUESTION 16
......
Thanks for reading the newest az-500 exam dumps! We recommend you to try the PREMIUM Surepassexam az-500 dumps in VCE and PDF here: https://www.surepassexam.com/az-500-exam-dumps.html (377 Q&As Dumps)
